SOC analyst training has quietly become one of the most practical doors into a stable, well-paid technology career this year. The reason is simple: ISC2’s Cybersecurity Workforce Study put the global cybersecurity workforce gap at roughly 4.8 million unfilled roles, even as ransomware incidents kept climbing to record levels.
Whether you’re switching over from IT support, finance, retail management, or the military, or you’re a recent graduate wondering how to become a SOC analyst, this guide walks through the real SOC analyst courses, the real cost, and the real career outcomes you can expect right now—not recycled statistics from three years ago.
What Does a SOC Analyst Actually Do?
A security operations center, or SOC, is the nerve center of an organization’s cyber defense. It’s the team that watches networks, endpoints, and cloud systems around the clock, hunting for signs that something has gone wrong. Good SOC analyst training teaches you how to work inside that nerve center: reading SIEM dashboards, triaging alerts, and escalating genuine incidents before an attacker causes real damage.
SOC analysts play a crucial role in handling cyberattacks, which is exactly why demand for this skill set keeps climbing as breaches grow more frequent and more costly. For many career changers, this is also the fastest realistic entry point into a full-time cybersecurity career.
Unlike a four-year computer science degree, structured SOC analyst training is built around one goal—getting you job-ready for entry-level SOC analyst roles within months, not years. A solid program blends theory (networking basics, operating systems, and log analysis) with hands-on labs that mimic real threat detection scenarios, so you graduate with practiced instincts rather than memorized answers.
You’ll also get an early introduction to vulnerability management, since spotting weaknesses before attackers do is central to the role. That hands-on approach matters, because employers in 2027 hire for demonstrated skill and portfolio work over a diploma alone.
How to Become a SOC Analyst: A 6-Step Roadmap
If you’re starting from zero, this is the order that works for most people, including those with no prior security experience:
-
Learn networking and OS fundamentals. TCP/IP, DNS, ports, Windows Event Logs, and basic Linux commands. You can’t investigate traffic you don’t understand.
-
Earn a baseline certification. CompTIA Security+ is the credential most entry-level SOC analyst job posts ask for. See our guide to the best SOC analyst certifications for the full path.
-
Get hands-on with a SIEM. Practice searching logs, building alerts, and triaging events in Splunk or Microsoft Sentinel. Structured Splunk training speeds this up.
-
Learn detection frameworks. Map alerts to MITRE ATT&CK tactics so you can explain why an event is suspicious, not just that it fired.
-
Build a portfolio. Document three to five investigations from a home lab or platforms like TryHackMe or LetsDefend, written up like real incident reports.
-
Prepare for interviews and apply. Practice walking through an alert out loud and review common SOC analyst interview questions before applying for Tier 1 roles.
Best SOC Analyst Training Programs and Courses in 2027
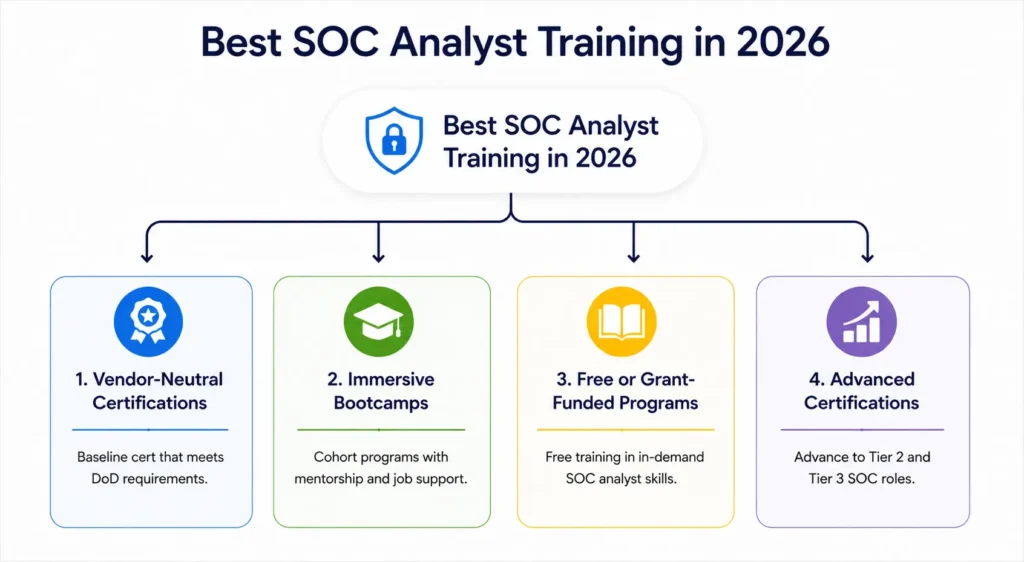
There isn’t one single path into this field, and that’s good news. Depending on your budget, timeline, and learning style, you can choose from several legitimate routes:
-
Vendor-neutral certifications such as CompTIA Security+ remain the baseline most employers look for, and it’s also the credential that satisfies DoD 8570/8140 requirements for government and defense contracting roles.
-
SOC analyst bootcamps like Springboard, Flatiron School, and Fullstack Academy compress six to twelve months of learning into focused, cohort-based programs with mentorship and job-search support.
-
Free SOC analyst training, including Per Scholas, CISA’s National Cyber Security Training Academy bootcamp, TryHackMe’s SOC Level 1 path, and LetsDefend, which teach threat detection, log analysis, and SIEM tools at little to no cost.
-
Advanced certifications such as CySA+ or GIAC’s GSOC, which build on Security+ and push you toward Tier 2 and Tier 3 blue team responsibilities.
Whichever path you pick, look for a SOC analyst course that includes a live SIEM lab (Splunk, QRadar, or Microsoft Sentinel), guided incident-response exercises, and interview coaching. Theory alone won’t get you hired in a market this competitive. Our SOC job seeker’s package bundles all three.
Choosing between an employer-sponsored track, a paid bootcamp, and a free program often comes down to timing. MSSPs hire heavily from grant-funded training pipelines because they need round-the-clock Tier 1 coverage, while in-house SOC teams at banks and healthcare systems prefer candidates who’ve already earned a recognized security certification. Either route can lead to a solid entry-level SOC analyst job, but research placement data before committing tuition money.
SOC Analyst Training Cost: What You’ll Actually Pay in 2027
Cost is where most people get confused, because pricing swings wildly depending on the format you choose. Here’s an honest breakdown based on current 2027 market pricing.
|
Training Path |
Typical 2027 Cost | Duration |
Best For |
|
CompTIA Security+ exam only |
$425–$439 | 2–4 months self-study |
Budget-conscious beginners |
|
Security+ with a structured course |
$700–$1,200 | 2–4 months |
First-timers wanting higher pass odds |
|
Grant-funded bootcamp (e.g., Per Scholas) |
Free (income-eligible) | 12–15 weeks |
Career changers with financial constraints |
|
Mid-tier bootcamp (Springboard, Nucamp) |
$2,100–$9,900 | 12–26 weeks |
Structured, mentor-backed learning |
|
Premium bootcamp (Flatiron, Fullstack) |
$14,995–$19,500 | 15–26 weeks |
Full-time, high-touch career support |
|
CySA+ / GIAC GSOC (advanced) |
$500–$2,000+ | 2–3 months |
Analysts moving to Tier 2/3 |
A single CompTIA Security+ voucher runs $425 to $439 in 2027, and most self-study candidates land a total cost between $600 and $1,000 once study materials are added. If you’d rather have a structured curriculum and job-placement support, SOC analyst bootcamps average roughly $10,600—a fraction of the $40,000-plus a four-year degree usually demands. Placement rates in credible programs cluster between 70% and 85% within twelve months of graduation, according to Hakia 2026 data.
If tuition is a genuine barrier, don’t overlook grant-funded options. Some cover the entire cost for income-eligible applicants and still include certification vouchers and hands-on SOC simulation. Programs that dedicate real lab hours to vulnerability management tend to show stronger Tier 2 placement outcomes than those that only cover theory.
Core SOC Analyst Skills You’ll Build During Training
A good program does more than prepare you for one exam. It builds a working toolkit you’ll rely on for years. Here’s what that typically covers, broken into the areas that matter most to hiring managers.
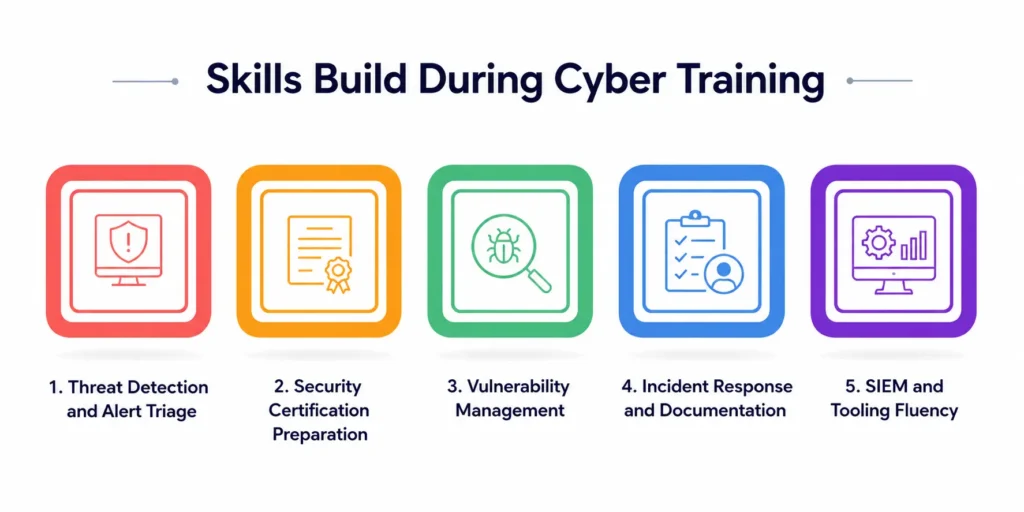
1. Threat Detection and Alert Triage
This is the daily bread of Tier 1 work—learning to separate genuine threats from the noise of false positives inside a SIEM platform, then deciding what deserves escalation. It’s a judgment call you’ll make dozens of times a shift, and it only sharpens with repetition.
2. Security Certification Preparation
Most programs build toward at least one recognized security certification, since certified analysts report earning meaningfully more than uncertified peers doing the same job.
3. Vulnerability Management
You’ll learn to scan environments, prioritize findings by real-world exploitability, and communicate risk to non-technical stakeholders—a skill that separates analysts from those who just run tools. Employers increasingly test this directly, asking candidates to walk through a real vulnerability backlog during the interview.
4. Incident Response and Documentation
Detecting an incident is only half the job. You also learn to contain it, document the timeline, and hand off clean reports that support both remediation and compliance audits.
5. SIEM and Tooling Fluency
Hands-on time with Splunk, Microsoft Sentinel, or QRadar turns theoretical knowledge into muscle memory you can demonstrate in an interview.
SOC Analyst Career Path and Salary in 2027
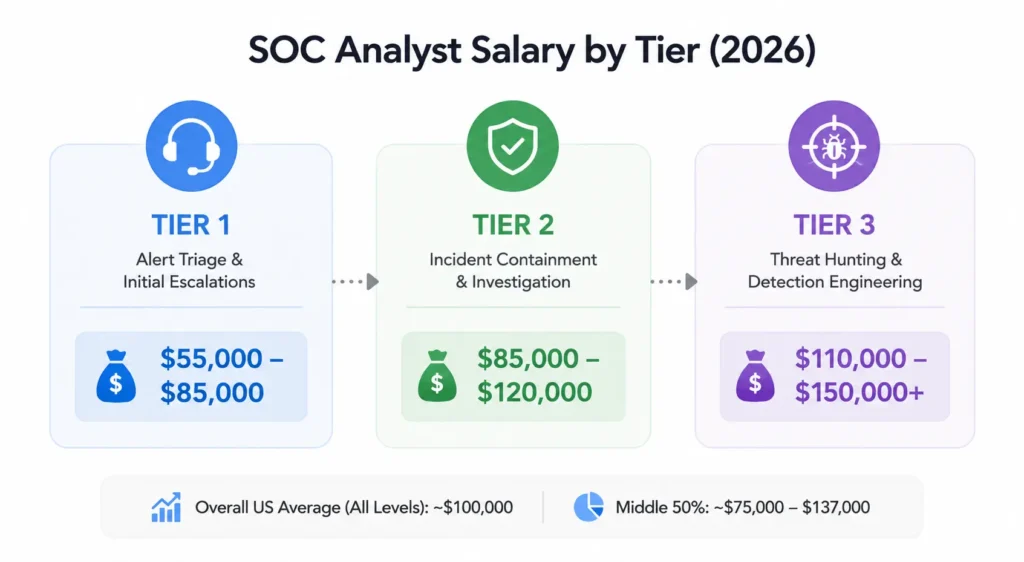
Once training is behind you, the SOC analyst career path is refreshingly linear compared to many tech fields. Most professionals move through recognizable tiers, and pay rises meaningfully at each step.
|
Tier |
Typical Role | Main Responsibility |
2027 US Salary Range |
|---|---|---|---|
|
Tier 1 (L1) |
Entry-level SOC analyst | Alert triage and initial escalation | $55,000–$85,000 |
| Tier 2 (L2) | Incident responder / investigator | Containment and deeper investigation |
$85,000–$120,000 |
|
Tier 3 (L3) |
Threat hunter / detection engineer | Proactive hunting and detection rules |
$110,000–$150,000+ |
The overall US average SOC analyst salary across all levels sits close to $100,000, with the middle 50% earning between roughly $75,000 and $137,000 a year. This tiered structure gives you a rare thing in tech: a clear, well-documented promotion ladder, where every step forward means deeper responsibility rather than a sideways move.
The demand side is what makes the investment worthwhile. The U.S. Bureau of Labor Statistics projects about 29% growth in information security analyst roles between 2024 and 2034, far faster than the average across all occupations.
That growth, paired with a global shortfall of skilled defenders, means employers are actively competing for candidates who can prove hands-on ability rather than just list credentials. If you’re weighing this against other tech paths, steady demand plus a clear promotion ladder is hard to beat in 2027.
A Personal Note From the Author
I want to be upfront about something: I didn’t start in cybersecurity. I spent my first few years doing general IT support, and I remember staring at a wall of SIEM alerts during my first week on a SOC floor, completely unsure which ones actually mattered. What changed things wasn’t a certification on paper—it was the lab hours.
I built my own home lab, broke it on purpose, and learned to read logs the way a mechanic learns to hear an engine problem before the dashboard warns them. Years later, when I sat in on hiring panels for junior analysts, the candidates who stood out weren’t necessarily the ones with the most certifications. They were the ones who could walk through a real alert, explain their reasoning out loud, and admit what they didn’t yet know.
Looking back, the training that stuck with me wasn’t the slide decks—it was breaking things at 11 p.m. and figuring out why. No certification alone can replicate that kind of stubborn curiosity. If you take one thing from my path, let it be this: treat every practice lab like a real incident, because that habit is what interviewers can actually see.
Final Thoughts
Breaking into this field in 2027 doesn’t require a perfect resume or a computer science degree. It requires a clear plan and consistent hands-on practice. Good SOC analyst training, whichever format you choose, should leave you able to walk into an interview and talk through a real alert with confidence, not just recite definitions.
Pair a recognized security certification with genuine lab hours, stay curious about how modern cyber defense keeps evolving alongside AI-assisted tooling, and treat vulnerability management and threat detection as skills you sharpen weekly, not topics you memorize once.
The skills gap isn’t closing anytime soon, which means the door into a SOC analyst career is wide open for anyone willing to put in the work. Start with one solid SOC analyst training path, finish it fully, and let your lab work do the talking in interviews.