One in four malicious data breaches in 2027 was AI-enabled, according to IBM’s latest Cost of a Data Breach report, and the average breach now costs $4.99 million globally and $11.5 million in the United States. Those numbers should make you pause. But here’s the harder question: if your organization got hit right now, would the person watching the monitor actually know what to do? That question is exactly why blue team certifications have become one of the most talked-about topics in cybersecurity hiring this year.
I still remember sitting for my own SOC analyst exam years ago, hands cold, wondering if a piece of paper could really prove I belonged in front of a SIEM dashboard at 2 a.m. It can, if you pick the right one. Companies are no longer willing to gamble on unproven defenders.
This guide compares the best blue team certifications for beginners and working analysts, with real 2027 exam costs, formats, and career fit, so you can choose with confidence instead of guesswork.
Quick answer: The best blue team certifications in 2027 are CompTIA CySA+ for a widely recognized, vendor-neutral credential; BTL1 or HTB CDSA for hands-on proof; Microsoft SC-200 or Splunk Cybersecurity Defense Analyst if your SOC runs those tools; and GIAC GCIH for incident response specialists. Complete beginners usually start with CompTIA Security+ or ISC2 CC.
Why Blue Team Certifications Matter More Than Ever in 2027
The shortage of skilled defenders is not a rumor. ISC2’s 2024 workforce study put the global cybersecurity workforce gap at 4.8 million people, and its 2025 study found the problem has shifted to skills: 95% of teams now report at least one critical skills gap. Meanwhile, attackers are using AI to write phishing emails, clone voices, and probe networks faster than most teams can react.
This mismatch is why organizations now treat defensive security certifications as a baseline requirement for anyone serious about security operations. Hiring managers use them as a quick filter, and certified professionals often earn more than uncertified peers doing similar work. They also tend to ramp up faster once they join a dedicated threat detection team.
It also helps to understand what these credentials actually test. Unlike red team certifications that focus on breaking into systems, blue team certifications validate your ability to monitor, detect, and respond to threats already inside, or trying to get inside, a network.
That includes log analysis, SIEM operations, threat intelligence, and structured incident response training, all skills a modern SOC analyst uses every single shift.
Cyber Defense Threats Driving the 2027 Certification Boom
Three trends are pushing demand for cyber defense talent higher than at any point in the last decade:
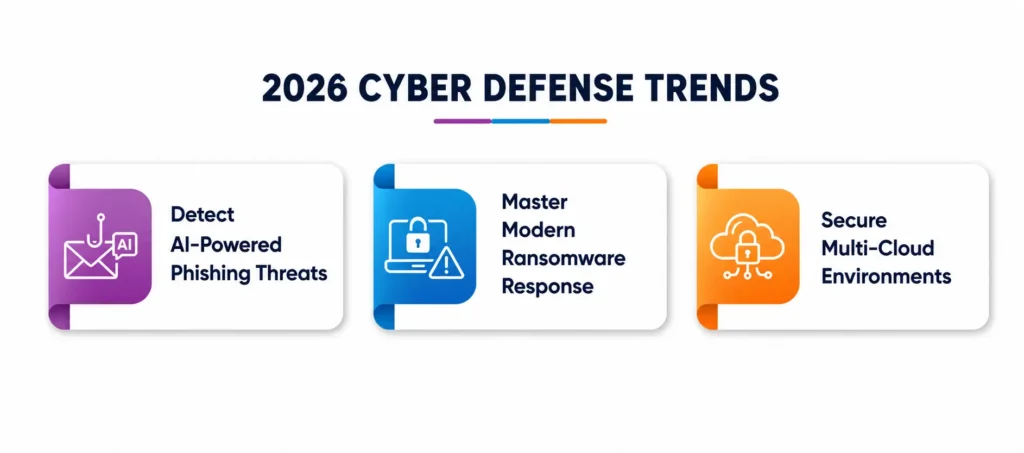
- AI-generated phishing and deepfake voice scams are bypassing traditional filters, forcing analysts to rely on behavioral threat detection rather than static rules.
- Ransomware groups are shifting toward double and triple extortion, which means incident response training now has to cover legal, PR, and recovery workflows, not just technical containment.
- Multi-cloud and hybrid work environments have multiplied the attack surface, so security operations teams need certifications that cover cloud-native logging alongside traditional network defense.
None of this is theoretical. It shows up in job postings every week, where employers ask for candidates who hold current cyber certifications tied to SIEM tools, cloud platforms, and incident handling frameworks like NIST and MITRE ATT&CK. A current SOC analyst certification is often one of the first things applicant-tracking software searches for before a human recruiter even opens the resume.
Best Blue Team Certifications Compared (Cost, Format, and Fit)
Choosing among today’s crowded field of cyber certifications gets easier once you see them side by side. The table below compares nine credentials that consistently show up in SOC and blue team job requirements for 2027.
|
Certification |
Issuing Body | Approx. Exam Cost (USD) | Format |
Best For |
|---|---|---|---|---|
|
CompTIA Security+ (SY0-701) |
CompTIA | About $425 to $439 | Multiple-choice + performance-based |
First certification; required for many entry-level and US government roles |
|
CompTIA CySA+ (CS0-004) |
CompTIA | About $425 to $439 | Multiple-choice + performance-based |
Analysts wanting a vendor-neutral, widely recognized SOC credential |
|
Blue Team Level 1 (BTL1) |
Security Blue Team | £399 (about $500 to $540), training included | 100% practical, 24-hour scenario exam |
Career changers who want hands-on proof over theory |
|
HTB Certified Defensive Security Analyst (CDSA) |
Hack The Box | About a $210 voucher (or included in the HTB Academy Silver Annual) | 7-day practical exam + written report |
Hands-on learners ready for intermediate SOC and DFIR work |
|
Microsoft SC-200 |
Microsoft | $165 | Proctored exam with case studies |
Analysts in Microsoft Sentinel and Defender XDR environments |
|
Splunk Certified Cybersecurity Defense Analyst |
Splunk | $130 | Online proctored exam |
Analysts working daily inside Splunk-based security operations |
|
Certified CyberDefender (CCD) |
CyberDefenders | Around $400 | 48-hour practical exam |
Working analysts wanting forensic and DFIR-heavy validation |
|
GIAC Certified Incident Handler (GCIH) |
GIAC / SANS | About $979 to $999 standalone; more with SANS SEC504 training | Proctored exam |
Professionals focused on formal incident response |
|
ISC2 Certified in Cybersecurity (CC) |
ISC2 | Paid since the free program closed on May 20, 2027 | Multiple-choice |
Complete beginners entering cyber defense from another field |
Notice the spread here. Some blue team certifications, like BTL1, HTB CDSA, and CCD, test you inside a simulated SOC where you investigate real artifacts under time pressure. Others, like Security+ and CySA+, lean more toward structured multiple-choice and scenario questions.
Neither approach is wrong. It depends on whether you learn better by doing or by studying frameworks first, and both sharpen the same core threat detection instincts employers are paying for.
If you only remember one thing from this comparison, remember that the strongest blue team certifications are the ones matched to how you actually work and learn, not the ones with the fanciest logo on the certificate.
Blue Team Certification Path: A Simple Roadmap
Most defenders progress through four stages:
-
Foundation: CompTIA Security+ or ISC2 CC.
-
Analyst: CompTIA CySA+, BTL1, or a tool-specific credential (SC-200, Splunk).
-
Hands-on intermediate: HTB CDSA, CCD, or BTL2.
-
Specialist: GIAC GCIH for incident response, or GIAC GSOC and GCIA for deeper SOC and intrusion analysis.
How to Pick the Right Blue Team Certification for Your Career Stage
There is no single “best” answer here, but there is a best answer for you, depending on where you currently stand.
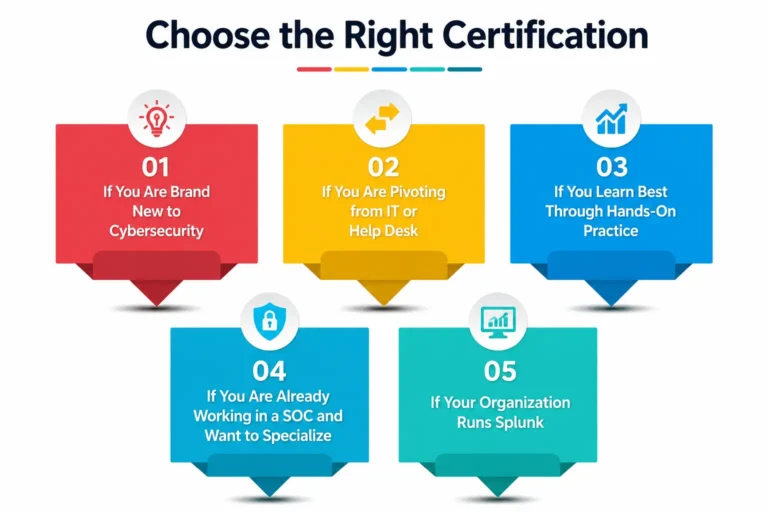
1. If You Are Brand New to Cybersecurity
Start with something foundational before committing money to a specialized exam. CompTIA Security+ is the most widely requested entry-level cybersecurity certification. ISC2 Certified in Cybersecurity is a lighter starting point; note that ISC2’s free exam program closed to new applicants on May 20, 2027, though anyone already holding a free exam code can test until December 31, 2027.
2. If You Are Pivoting from IT or Help Desk
CompTIA CySA+ is usually the strongest next step. It is vendor-neutral, widely requested in job listings, and pairs well with prior Security+ knowledge without demanding years of specialized experience. The current version is CS0-004, launched in June 2027.
3. If You Learn Best Through Hands-On Practice
BTL1, HTB CDSA, or the Certified CyberDefender credential will suit you better than a multiple-choice exam. All three simulate real scenarios, forensic artifacts, and log analysis under realistic time pressure.
4. If You Are Already Working in a SOC and Want to Specialize
GIAC’s GCIH remains a gold standard for incident handling, especially if your employer is funding the accompanying SANS SEC504 course. It carries serious weight with hiring managers in regulated industries. If your focus is day-to-day SOC operations rather than incident handling, look at GIAC GSOC, which pairs with the SANS SEC450 course.
5. If Your Organization Runs Splunk or Microsoft Sentinel
The Splunk Certified Cybersecurity Defense Analyst credential is inexpensive and directly tied to the tool you likely already use daily. If your SOC runs Microsoft Sentinel and Defender XDR, Microsoft SC-200 does the same job for that stack. Either is a quick, practical addition to your resume.
What Do Employers Actually Look For in 2027?
Employers rarely hire based on a single badge. What they want is evidence that you can walk into a live environment and function immediately. That is why job postings increasingly pair a named credential with phrases like “hands-on SIEM experience” or “documented response experience.”
A certification proves baseline knowledge; a home lab, a blog write-up, or a practice-platform portfolio proves you can apply it. Combining a recognized credential with visible, practical work consistently outperforms a resume listing five cyber certifications and nothing else.
Salary data from HackTheBox’s 2026 report backs this up. Entry-level SOC analysts in the United States earn around $102,000 on average, with a typical range between $75,000 and $140,000, while incident response specialists average around $108,000.
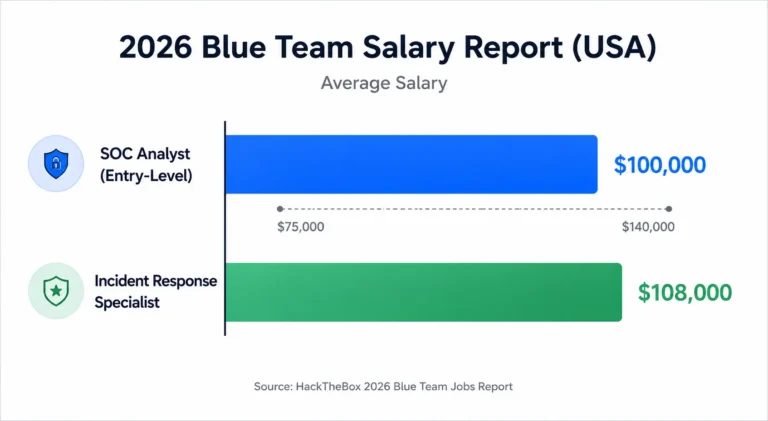
Threat intelligence analysts, who rely heavily on advanced detection skills, often clear $148,000. None of these figures are guaranteed by a certificate alone; they reflect certified professionals who also built real, demonstrable skill.
Employers filling security operations seats often list a SOC analyst certification as the minimum bar, then look for genuine threat detection instincts and completed incident response training layered on top before they extend an offer.
Building Real Skills to Back Your Blue Team Certification
A single certification looks good on paper, but hiring managers in 2027 want proof you can apply it under pressure. Set up a free-tier SIEM such as Splunk or Elastic and practice basic threat detection: hunting failed logins, unusual outbound traffic, and privilege escalation attempts in sample data sets. Our Splunk training is one structured way to do this.
Volunteer for shadow shifts inside a security operations center if your current employer has one, even informally, so the workflow feels familiar before your first real shift alone. Document what you learn in a public blog post or a small repository of write-ups. This single habit does more for your credibility than a stack of unused cyber certifications ever could.
Pairing structured incident response training with a home lab built around realistic cyber defense scenarios shows employers you understand both the theory and the pressure of the job, not just the vocabulary.
This is also where some of the strongest blue team certifications distinguish themselves: BTL1, HTB CDSA and the CyberDefenders Certified CyberDefender program bake hands-on problem-solving directly into the exam itself, so preparation and genuine skill-building happen at the same time rather than in separate stages.
A Quick Personal Note
When I first moved from a general IT support role into a security operations team, I made the mistake of chasing every acronym I could find, thinking more letters after my name would fix my confidence gap. What actually got me hired was pairing one solid, practical credential with a home lab where I documented real exercises and shared them publicly.
The certification opened the interview door; the visible practice closed it. If you take one thing from my own path into this field, let it be this: pick one certification that matches how you learn, then spend just as much energy proving you can use it.
Conclusion: Choosing Your Blue Team Certification
Choosing among today’s blue team certifications does not have to feel overwhelming once you match the credential to your actual career stage rather than chasing prestige. Beginners benefit from Security+ or ISC2 CC, career switchers gain the most from CompTIA CySA+, hands-on learners thrive with BTL1, HTB CDSA or CCD, tool-focused analysts should look at SC-200 or Splunk, and working analysts aiming for specialization should look toward GIAC’s incident response path.
Whichever route you choose, treat your certification as a starting point, not a finish line. Pair it with real lab work, and you will stand out in a field where demand for skilled defenders still far outpaces supply. If you want a guided route, our SOC Job Seeker’s Package combines training, labs and interview prep.