A few years ago, a friend of mine—fresh out of a commerce degree, no coding background, no tech family—messaged me asking if it was “too late” to get into cybersecurity. She thought she’d need a computer science degree and years of savings just to get a foot in the door.
Turns out, that’s one of the biggest myths floating around this industry. Today, an information security training course is more accessible, more affordable, and more beginner-friendly than it has ever been—and you can take most of them as a cybersecurity course online, from home, at your own pace.
If you’re a student, a career switcher, or just someone tired of hearing about data breaches on the news and wanting to actually understand what’s going on—this guide is for you. We’ll walk through what information security training actually involves, why it matters right now, which free and paid cybersecurity courses for beginners are worth your time, and how to find one that won’t drain your savings.
Why Information Security Training Matters More Than Ever
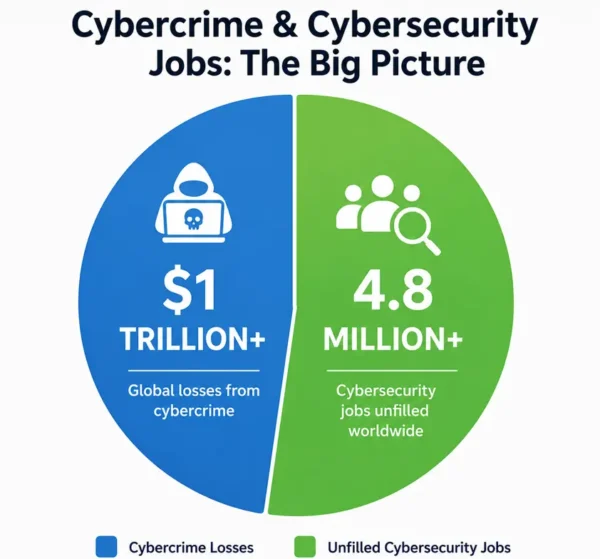
Cybercrime isn’t some distant, abstract threat anymore. Global cybercrime losses now run into the trillions of dollars every year [add source link], and according to ISC2’s 2024 Cybersecurity Workforce Study, the global cybersecurity workforce gap reached roughly 4.8 million unfilled positions [add source link]. Read that again—nearly five million jobs sitting empty because there simply aren’t enough trained people to fill them. That’s not a “maybe you’ll find work” situation. That’s an industry practically begging for skilled hands.
This is exactly why information security training has become one of the most in-demand skill areas for students across the world, regardless of whether you come from an IT background or not. Employers today aren’t just looking for people with fancy degrees—they want people who understand the fundamentals, can think like an attacker, and know how to defend systems in the real world.
Whether your goal is a corporate job, freelance consulting, or simply protecting your own business or personal data, this kind of learning gives you a foundation that applies everywhere—from banking to healthcare to e-commerce.
What Does a Good Information Security Training Course Actually Cover?
Not all information security courses are created equal, and honestly, a lot of “cheap” courses out there are just recycled slides with outdated screenshots. A genuinely useful information security training program should walk you through a logical progression, not just throw jargon at you.
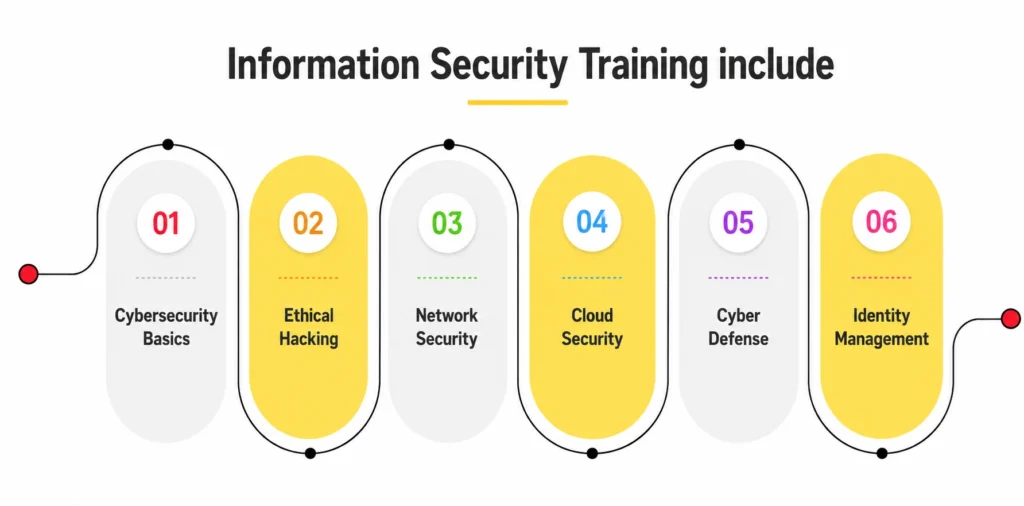
Here’s what a well-structured cybersecurity course typically includes:
1. Cybersecurity Basics
Every solid program starts here. You’ll learn about threats, vulnerabilities, risk management (link: RMF course), malware types, phishing, and the everyday habits that keep systems safe. You’ll also meet the CIA triad—confidentiality, integrity, and availability—the core idea behind all of information security. Think of this as your foundation—you can’t build a house without it, and you can’t understand advanced topics without grasping these fundamentals first.
2. Ethical Hacking
This is the part most students get excited about. Ethical hacking (link: ethical hacker certification cost) teaches you to think like an attacker so you can defend like a professional. You’ll get hands-on with tools like Nmap and Metasploit, learn about penetration testing, and understand how real breaches happen. Employers also prize mastery of frameworks such as MITRE ATT&CK and tools like Metasploit and Wireshark, so if a course skips these entirely, that’s a red flag.
3. Network Security
Since almost every attack travels across a network at some point, understanding network security—firewalls, VPNs, intrusion detection systems, and secure protocols—is non-negotiable. A good course will have you configuring basic security controls in hands-on labs, not just reading about them, so you actually understand how traffic moves and where it can be intercepted.
4. Cloud Security
With most companies now running on AWS, Azure, or Google Cloud, cloud security has become a must-have skill rather than a nice-to-have. It includes identity policies, encryption in cloud environments, and understanding shared responsibility models between you and your cloud provider—because in the cloud, security is never fully handled by just one side.
5. Cyber Defense and Security Operations (SOC)
This is where everything comes together: incident response, threat detection, SIEM tools like Splunk, and building resilient systems. Good defensive training teaches you not just how to prevent attacks but how to respond when something does go wrong, because eventually, something will, and the speed of your response often matters more than the attack itself.
6. Identity and Access Management (IAM)
Often overlooked but critically important. This domain covers how organizations control who has access to what—think multi-factor authentication, single sign-on, and access control policies. Weak controls in this area are behind a huge chunk of real-world breaches, so it deserves proper attention in any course you pick, even if it sounds less exciting than hacking labs.
7. Governance, Risk, and Compliance (GRC)
Not every information security job is technical. Frameworks like ISO 27001, NIST, and SOC 2 decide how companies manage security on paper and in audits. A short GRC module opens the door to IT audit and compliance roles, which suit people from commerce or business backgrounds—like my friend.
Free vs. Paid Cybersecurity Courses: What’s Actually Worth Your Money?
Here’s the good news—you genuinely don’t need to spend a fortune to get quality information security training today. Some of the best entry points into this field cost very little, and a few free cybersecurity courses even come with a certificate.
The standout example is the ISC2 Certified in Cybersecurity (CC) credential (link: isc2.org). Since August 2022, ISC2 reduced financial barriers for more than 1 million people across 178 countries through its One Million Certified in Cybersecurity program, which offered a free online course and a free exam. That program stopped accepting new participants on May 20, 2027. If you already have an unexpired exam code, you can still schedule and sit the exam until December 31, 2027.
For everyone starting fresh now, the ISC2 CC exam costs $199 plus a $50 annual maintenance fee—still one of the most affordable entry-level cybersecurity certifications on the market, especially compared to something like CISSP, which requires years of prior experience.
Beyond ISC2, there’s a whole ecosystem of low-cost and free learning options:
- Courses from Cisco Networking Academy, IBM Skills Build and Fortinet are free and include certificates or badges, which is great news if budget is your main concern.
- The Google Cybersecurity Certificate on Coursera covers core concepts like threat identification, secure network fundamentals, and SIEM basics. It requires a Coursera subscription unless you qualify for financial aid.
- Learning platforms such as Coursera, edX, and Cybrary list thousands of information security courses, many free, spanning everything from digital forensics to ISO 27001 compliance.
ISC2 CC vs CompTIA Security+: Which Entry-Level Certification First?
This is the question beginners ask most. ISC2 CC is cheaper and easier, and it is a good first credential to prove you understand the basics. CompTIA Security+ costs more (roughly $400+ per exam voucher) [verify current price], goes deeper, and is the certificate most entry-level job postings and US DoD roles ask for. A practical path: learn the fundamentals, earn CC if the budget is tight, then move to Security+ once you are sure cybersecurity is for you.
Quick Comparison Table: Best Information Security Courses Online
|
Course Type |
Best For | Approx. Cost |
Focus Area |
|---|---|---|---|
|
ISC2 Certified in Cybersecurity (CC) |
Absolute beginners wanting a recognized credential | $199 exam + $50/year (free vouchers closed to new sign-ups) |
Security fundamentals, access control, secure networking |
|
CompTIA Security+ |
Beginners targeting entry-level job postings | Roughly $400+ per voucher [verify] | Threats, architecture, operations, incident response |
| Google Cybersecurity Certificate (Coursera) | Students wanting structured, guided learning | Coursera subscription (financial aid available) |
Threat basics, SIEM, Python, Linux |
|
Cisco, IBM SkillsBuild, and Fortinet free courses |
Budget-conscious learners | Free |
Firewalls, defense operations |
|
ThinkCloudly Cyber Security course and Job Seeker’s Package |
Career switchers wanting live mentorship, labs, and job support | Paid (see course page) |
SOC, network and cloud security, hands-on labs, interview prep |
|
University online cybersecurity degrees (e.g., Bellevue) |
Long-term career builders wanting a formal degree | Per-credit tuition, often discounted for online/military learners |
Full-spectrum technical and defensive skills |
Tips for Choosing the Right Information Security Training Course
Since there are literally thousands of options out there, here’s how to filter through the noise:
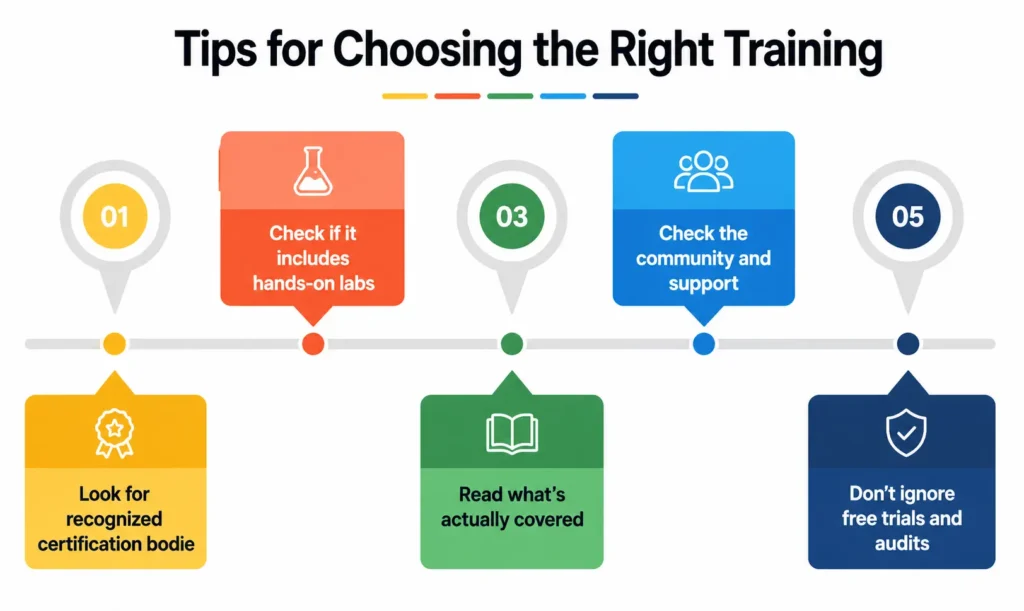
1. Check if it includes hands-on labs.
Watching videos is fine for theory, but information security training without practical labs won’t prepare you for real-world scenarios or interviews.
2. Look for recognized certification bodies.
Courses aligned to ISC2, CompTIA, ISACA, or Cisco certifications carry more weight with employers than random platforms you’ve never heard of.
3. Read what’s actually covered.
A course that only skims cybersecurity basics without touching offensive security techniques, cloud environments, or access controls is incomplete for today’s job market.
4. Check the community and support.
Learning alone is hard. Courses with active forums, mentor access, or peer groups tend to keep students motivated longer.
5. Don’t ignore free trials and audits.
Many paid platforms let you try content for free before committing money—use this to test if the teaching style actually works for you.
6. Ask about job support
A certificate alone rarely gets you hired. Look for a course that also offers resume reviews, mock interviews and real project work you can show employers.
Learn Information Security Online with ThinkCloudly
If you want structure instead of piecing together free videos, ThinkCloudly’s Complete Cyber Security Course (link) is built for beginners and career switchers. You learn through instructor-led sessions and hands-on labs, covering network security, cloud security, SOC operations and incident response. For a job-focused path, the Cyber Security Job Seeker’s Package (link) and SOC Analyst training (link) add interview preparation and resume support. Not sure where to start? Take the free assessment (link) or book a free career counselling session.
How to Get Into Cybersecurity With No Experience
Yes, it’s realistic—and this is one of the few tech fields where a formal degree isn’t a hard requirement. Practical skills, certifications, and demonstrated hands-on ability often matter just as much, sometimes more, than a diploma. Combining structured coursework with real project work (even personal ones, like setting up a home lab or practicing on platforms like TryHackMe or Hack The Box) can make your resume stand out significantly.
Given the workforce shortage we mentioned earlier, students who invest time now — even through free or low-cost cybersecurity courses for beginners — are positioning themselves ahead of a massive hiring curve.
What Cybersecurity Jobs Can Information Security Training Lead To?
One thing students often ask is what happens after the course—what job titles are actually realistic once you’ve completed your information security training. The honest answer is that the field is wide, and where you land depends on which supporting skill you lean into.
If you enjoyed the offensive side of things, roles like penetration tester or vulnerability analyst build directly on offensive-security skills, along with a working grasp of identity management since attackers so often target weak access controls first. If configuring firewalls and monitoring traffic feels satisfying, secure networking engineer (link) or SOC (Security Operations Center) analyst roles are a natural next step.
Students who found themselves drawn to the cloud security modules often move toward cloud security engineer or DevSecOps roles (link), which are among the fastest-growing and best-paid tracks in the industry right now, given how quickly companies are shifting infrastructure to the cloud.
For those who liked the “big picture” thinking—risk, response, and resilience—incident response analyst or GRC and IT audit roles fit well. And if the access-control and governance side appeals to you more than hands-on technical work, IAM (Identity and Access Management) specialist roles are growing steadily, especially as companies scramble to secure remote and hybrid workforces. Later, management-track certifications like CISM (link) and CISSP become the next step.
The point is: you don’t need to master every single track. Most professionals specialize after building a strong foundation, and that foundation is exactly what a good entry-level information security training course is designed to give you.
A Personal Note
I’ll be honest with you—when I first started exploring this space for people around me, I expected it to be intimidating, gated behind expensive bootcamps and years of prerequisites. What actually surprised me was how much genuinely good, free, and low-cost information security training exists right now, if you know where to look.
My honest advice? Don’t wait for the “perfect” course or the “right time.” Start with something free, get your hands dirty, and let curiosity pull you forward. The field rewards people who show up consistently far more than people who wait for permission.