Yes—CRISC certification is worth it in 2027 if you have (or will soon have) three years in IT risk, audit, or GRC and want to move into risk management leadership. It is not worth it for entry-level candidates or hands-on technical specialists with no interest in governance.
CRISC certification has become one of the sharpest career moves a risk professional can make right now—and the market proves it.
Boards are demanding structured risk governance programs. Regulators are penalizing organizations that cannot demonstrate documented IT risk assessment processes. AI-powered attacks and supply chain threats have pushed cybersecurity risk out of the IT department and into the boardroom. The result is a growing gap between demand for qualified IT risk professionals and the talent available.
In this guide you will find everything you need to decide: what the credential covers, the full CRISC certification cost, what it pays by role and region, how CRISC compares with CISA, CISM, and CISSP, and a direct verdict for your career stage. No filler—just what matters.
What Is CRISC Certification?
CRISC—Certified in Risk and Information Systems Control—is issued by ISACA and is the most recognized IT risk management certification for professionals working where technology and business risk meet.
Launched in 2010, CRISC was built to close a specific gap: organizations needed professionals who could connect IT risk assessment to real business outcomes, not just manage technical controls. Today it is held by tens of thousands of professionals worldwide and remains the only major certification purpose-built to bridge IT risk and business strategy.
The CRISC exam domains (ISACA’s 2025 exam content outline, effective 3 November 2025):
- Governance (26%) — Building risk governance frameworks aligned with enterprise strategy
- Risk Assessment (22%) — Identifying threats, evaluating vulnerabilities, measuring business impact
- Risk Response and Reporting (32%) — Designing treatment plans and communicating risk to stakeholders
- Technology and Security (20%) — Understanding the controls and security architecture that underpin risk management
The 32% weight on risk response and reporting signals what the credential values most: not just identifying risk, but knowing what to do with it—and explaining it clearly to decision-makers.
Why CRISC Carries More Weight in 2027
Three converging forces are pushing demand for CRISC-certified professionals higher than at any point since the credential launched.
Rising Cybersecurity Risk Is Reshaping Demand
The threat landscape has fundamentally shifted. Ransomware-as-a-service, AI-powered phishing, and supply chain compromises have made cybersecurity risk a business-level exposure, not a back-office IT problem. Organizations need professionals who can evaluate these threats in financial and operational terms—exactly the role CRISC is built for.
Stricter Compliance Requirements
Regulatory pressure is tightening globally. GDPR, ISO 27001, the NIST Cybersecurity Framework, and the EU’s Digital Operational Resilience Act (DORA, in effect since January 2025) all require documented risk assessment processes, formal risk response plans, and clear accountability. Companies that cannot demonstrate structured enterprise risk programs face legal and financial consequences. CRISC-certified professionals build those programs.
Risk Governance Is Now a Boardroom Priority
Risk governance has moved from a back-office function to a C-suite responsibility. CISOs present to audit committees. Chief Risk Officers sit on executive leadership teams. Quarterly risk reporting is becoming standard at public companies following the SEC’s 2023 cybersecurity disclosure rules. Professionals who can translate IT risk into business language—the core of what CRISC teaches—are the ones advancing into leadership.
What Skills Does CRISC Build?
Unlike certifications that lean heavily on theory, CRISC is built around skills you use on the job.
IT Risk Assessment
CRISC builds a systematic, repeatable method for evaluating IT risk—asset inventories, threat modelling, vulnerability analysis, and impact quantification—that holds up under regulatory scrutiny. This matters as organizations run multi-cloud environments and complex vendor ecosystems where ad hoc assessment does not scale.
Risk Mitigation Strategies
CRISC covers the full risk response decision tree: when to apply controls, when to transfer risk through insurance or contracts, when to accept it and when to avoid it entirely. It also covers incident response planning and monitoring control performance over time—skills that map directly to daily GRC work. You move from reactive problem-solver to proactive risk architect.
Risk Governance and Reporting
Building a risk register is easy. Building a risk governance program that survives audits, leadership changes, and regulatory reviews is genuinely hard. CRISC trains you to set up governance frameworks with clear ownership, defined escalation paths, and reporting that keeps risk visible at the right levels.
Aligning Risk with Business Objectives
The most undervalued skill CRISC develops is translating IT exposure into financial and strategic terms. Professionals who quantify risk as business impact are far more effective in executive conversations than those who only cite technical severity scores. This is the capability that opens executive doors.
CRISC Exam Details and Requirements (2027)
|
Exam Component |
Details |
|---|---|
|
Exam questions |
150 multiple-choice questions |
|
Duration |
4 hours |
|
Passing score |
450 out of 800 (scaled) |
|
Exam fee |
$575 (ISACA members) / $760 (non-members) |
|
Experience requirement |
3 years across at least 2 domains; 1 must be governance or risk assessment |
|
Experience waivers |
None—CRISC allows no substitutions. |
|
CPE maintenance |
120 hours over 3 years; minimum 20 hours a year |
You can sit the CRISC exam before meeting the experience requirement. Once you pass, you have five years to submit verified experience for full certification—a useful strategy if you are still building your GRC background.
One mindset note: the exam tests the ISACA way of thinking. Real-world practice does not always match the textbook answer. On exam day, default to the prescribed framework, not your organization’s custom approach.
How Much Does CRISC Certification Cost?
The exam fee is only part of the CRISC certification cost. Budget for the full picture:
|
Cost item |
ISACA member |
Non-member |
|---|---|---|
|
Exam registration |
$575 |
$760 |
|
Annual maintenance fee |
$45 |
$85 |
|
ISACA membership (optional) |
~$135/year + chapter dues |
— |
|
Study materials / training |
$300–$1,500 depending on route |
$300–$1,500 |
|
Typical total (first year) |
$1,500–$2,500 |
$1,500–$2,500 |
If you plan to keep the credential, membership usually pays for itself through the lower exam and maintenance fees. Many employers sponsor the full cost—ask before you pay out of pocket.
CRISC Salary in 2027
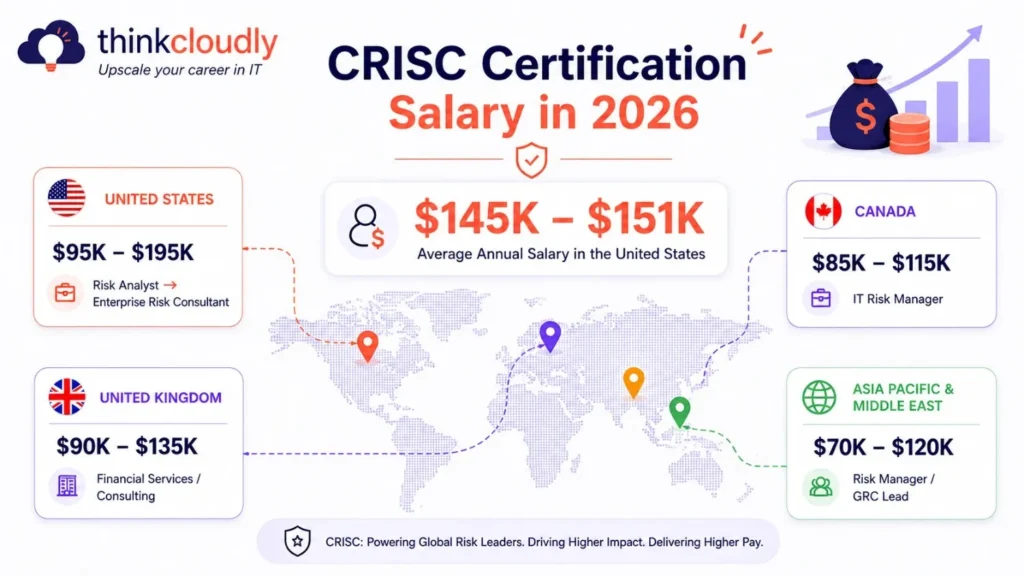
CRISC consistently ranks among the top-paying IT certifications. According to ISACA and PayScale data, the average CRISC holder in the United States earns between $145,000 and $151,000 a year.
CRISC Salary by Role and Region
|
Region |
Role |
Average Annual Salary (USD) |
|---|---|---|
|
United States |
Risk Analyst |
$95,000 – $120,000 |
|
United States |
IT Risk Manager | $130,000 – $165,000 |
| United States | Information Security Manager |
$140,000 – $175,000 |
|
United States |
GRC Specialist | $110,000 – $145,000 |
| United States | Enterprise Risk Consultant |
$150,000 – $195,000 |
|
Canada |
IT Risk Manager | $85,000 – $115,000 (Toronto/Vancouver lead) |
| United Kingdom | Financial Services / Consulting |
$90,000–$135,000 (London at the upper end) |
|
Asia Pacific |
IT Risk Manager / GRC Lead |
$70,000 – $110,000 (Singapore/Sydney lead) |
|
Middle East |
GRC Specialist / Risk Manager |
$80,000 – $120,000 (UAE/Saudi Arabia) |
In high-demand markets—New York, London, Singapore, Toronto, and Dubai—figures run 20–30% above regional averages. Financial services and healthcare pay at the top of the range because of regulatory intensity.
What Drives a Higher CRISC Salary
The biggest levers beyond the credential itself are experience (compensation accelerates after about 8 years in risk management), industry, and credential stacking. Pairing CRISC with CISM or CISA is a strong move for GRC Director and CISO-track roles, and holders of that combination report the highest pay. With a typical total investment of $1,500–$2,500, the cost is often recovered within the first year of a resulting raise or promotion.
CRISC vs CISA vs CISM vs CISSP
|
Certification |
Issuer | Primary Focus |
Best For |
|---|---|---|---|
|
CRISC |
ISACA | IT risk assessment and risk governance |
Risk managers, GRC professionals |
|
CISA |
ISACA | IT auditing and control assessment |
IT auditors, internal audit teams |
|
CISM |
ISACA | Information security management |
Security managers, program leaders |
|
CGEIT |
ISACA | IT governance aligned to business |
IT governance executives |
|
CISSP |
ISC2 | Broad security across 8 domains |
Security architects, security leaders |
CRISC vs CISA: Choose CRISC when your work centers on building and governing risk programs rather than auditing existing controls. CISA answers, “Are the controls working?” CRISC answers, “Do we have the right controls?”
CRISC vs CISM: Choose CRISC to specialize in risk quantification and compliance-focused risk programs; choose CISM for broad security program management. Many senior GRC professionals hold CRISC alongside CISA or CISM, and the pair is common at director level.
CRISC vs CISSP: CISSP is broader and more technical and requires five years of experience. CRISC is narrower and business-focused. They stack well: ISC2 accepts CRISC as one of the credentials that can waive one year of the CISSP experience requirement.
CRISC Career Path: Roles and Progression
CRISC is most valuable at the career turning points where a credential opens doors that experience alone will not.
Typical risk analyst career path:
- IT Auditor / Junior Risk Analyst
- Risk Analyst
- Senior Risk Analyst
- IT Risk Manager
- GRC Director
- Chief Risk Officer (CRO)
CRISC speeds up the move from Senior Risk Analyst to IT Risk Manager, and from IT Risk Manager to GRC Director — the transitions where hiring managers actively screen for it. Other common CRISC jobs include Cyber Risk Manager, Vendor Risk Manager, Third-Party Risk Analyst, Governance & Compliance Specialist and Enterprise Risk Manager.
One emerging angle: professionals who pair CRISC’s GRC foundation with cloud knowledge — especially AWS fundamentals and cloud-native risk controls — are landing the most competitive GRC roles. In 2027, cloud fluency is fast becoming what separates good candidates from great ones.
Who Should Pursue CRISC Certification?
CRISC delivers strong ROI for the right professional — and a poor one for the wrong fit.
Ideal For
- IT auditors with CISA looking to move into enterprise risk strategy
- Cybersecurity professionals targeting CISO or GRC leadership roles
- Risk analysts in financial services, healthcare or government contracting
- GRC consultants who need credentials to build client credibility
- Compliance specialists managing regulatory risk programs
Not Ideal For
- Professionals with fewer than 3 years of relevant experience (start with an entry-level GRC certification instead)
- Hands-on specialists in penetration testing or security engineering with no interest in governance
- Developers or IT generalists who have not worked in risk-adjacent roles
Pros and Cons of CRISC Certification
Pros
- Global recognition in 180+ countries, backed by ISACA
- Above-market pay — certified professionals consistently earn more than non-certified peers
- Practical frameworks that map directly to real GRC responsibilities
- Executive visibility — signals the risk governance fluency boards value
- Relative scarcity — far fewer holders than CISA or CISSP, against rising demand
Cons
- Experience barrier — the three-year requirement is a real gate, with no waivers
- Total cost of $1,500–$2,500 without employer sponsorship
- Ongoing CPE hours and annual fees add workload
- Exam mindset shift — real-world practice often differs from ISACA’s prescribed answers
So, Is CRISC Worth It in 2027?
The answer depends on your role and where you want to go.
For IT Auditors
This is one of the strongest moves you can make. Auditing verifies whether controls work. Risk management decides whether the right controls exist at all. CRISC moves you upstream — from reactive verification to proactive strategy — and CISA + CRISC is the combination many GRC director job postings ask for.
For Cybersecurity Professionals
Technical skills hit a ceiling without business risk fluency. The people advancing to CISO and GRC Director roles can turn a cybersecurity risk assessment into a risk-adjusted business recommendation. CRISC builds exactly that, and it is the most direct employer-recognized way to show readiness for cyber risk leadership.
For Risk Managers
At the senior level in 2027, CRISC is close to a baseline expectation. Major financial institutions, healthcare systems and consulting firms screen for it in mid-to-senior hiring. Even for experienced practitioners, its structured risk assessment and risk response frameworks add real value — especially in multi-vendor environments.
Final Verdict
CRISC is not a shortcut. It demands real experience, a deliberate financial investment and sustained effort to maintain. But for the right professional the return is clear: higher pay, faster advancement and access to leadership roles that non-certified peers struggle to reach.
If your goal is proven expertise in IT risk assessment, risk governance, cybersecurity risk management and business risk strategy — with credibility at executive level — CRISC remains the strongest IT risk management certification available in 2027.