I still remember the first time someone asked me to explain what “GRC” even stood for. I fumbled through governance, risk, and compliance like I was reciting a spelling bee word I’d only half-memorized.
A few years and a lot of trial and error later, I’ve watched dozens of career switchers, some fresh out of college, some coming from customer service or accounting, land their first GRC analyst jobs with no experience and without a single line of “risk analyst” on their resume.
If you’re wondering how to become a GRC analyst from zero, I want to walk you through exactly how people do it, because I’ve seen the pattern repeat often enough to trust it.
This isn’t a fluffy “just believe in yourself” post. It’s a practical map: what entry-level GRC analyst roles actually pay, which skills matter, which certifications are worth your money, and how to position yourself so a hiring manager stops seeing “no experience” and starts seeing “someone I can train fast.”
What Does a GRC Analyst Actually Do?
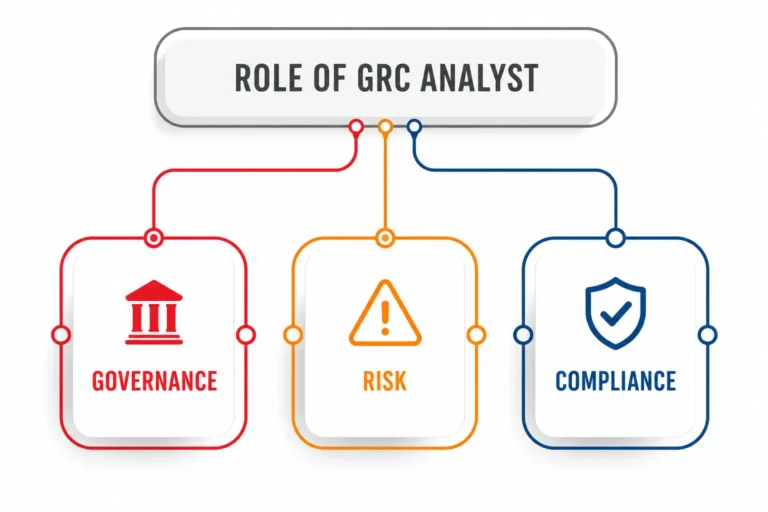
A GRC analyst (governance, risk, and compliance analyst) makes sure an organization’s security and business practices line up with laws, standards, and internal policy. Before chasing GRC analyst jobs, it helps to know what you’re signing up for. The role sits at the intersection of three things:
- Governance: making sure the organization has policies and decision-making structures that actually work
- Risk: identifying what could go wrong and how badly
- Compliance: proving the company follows the laws and standards it’s supposed to, such as SOC 2, ISO 27001, HIPAA, or GDPR
In practice, that means writing policy documents, running risk assessments, tracking audit findings, and translating dense regulatory language into something a business team can act on. It’s less “hacker in a hoodie” and more “detective with a spreadsheet. ” If you like structure, documentation, and asking “But how do we know that’s actually true?” you’ll probably enjoy this work. No coding is required for most entry-level GRC roles.
How Much Does an Entry-Level GRC Analyst Make?
The pay is solid for a role that accepts career switchers. Salary sites put the average GRC analyst salary in the United States at around $77,403 per year as of July 2027, with entry-level pay (10th percentile) starting near $50,802.
Other data is more encouraging for newcomers. As of mid-2027, one salary aggregator lists the average entry-level GRC analyst salary at $80,350 a year, or roughly $38.63 an hour, with the middle 50% earning between $54,000 and $100,500.
ERI SalaryExpert is more conservative: an entry-level GRC analyst with one to three years of experience earns an average of $63,297, while senior professionals with eight or more years earn around $100,606, based on SalaryExpert’s 2026 compensation data.
All three sources agree on one thing: the range is wide. Where you land depends on your certifications, your specialization, and how well you talk about risk in business terms rather than jargon.
In our GRC analyst salary guide, we found that analysts who pair compliance work with a technical understanding of cybersecurity controls can earn $20,000 to $30,000 more per year than those focused only on paperwork.
Why “No Experience” Doesn’t Mean “No Chance” in GRC
Here’s the part that surprises people: GRC is one of the few corporate career paths where a strong foundation in frameworks can outweigh years of unrelated job titles. Employers care less about your past title and more about whether you can read a policy, spot a gap, and document it clearly.
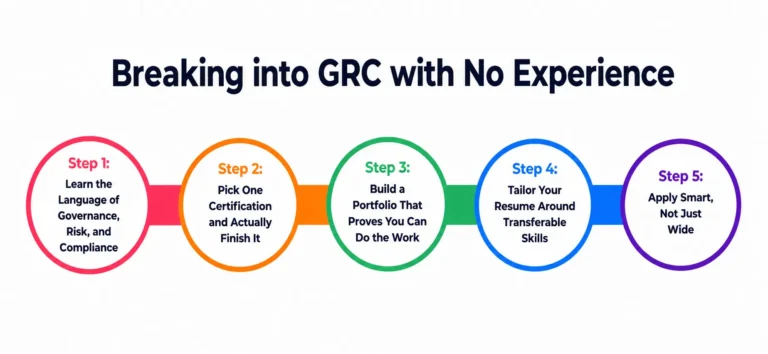
I won’t sugarcoat it. Plenty of postings for GRC analyst jobs still ask for “2-3 years experience” out of habit, even for junior roles. The trick isn’t to argue with that line item. It’s to build a resume and portfolio that make the requirement feel irrelevant. The five steps below are how most people become a GRC analyst with no experience.
Step 1: Learn the Language of Governance, Risk, and Compliance
You don’t need a cybersecurity degree to start. You need fluency in the vocabulary recruiters scan for. Spend real time understanding:
- How a governance framework is structured: policies, standards, and procedures, and how they cascade down from leadership
- Core risk management concepts like likelihood, impact, risk appetite, and risk registers
- The basics of regulatory compliance: why laws like GDPR, HIPAA, or SOX exist and what they require companies to do
- What a compliance audit looks like from start to finish, including evidence collection and remediation tracking
- How common frameworks compare: NIST CSF, ISO 27001, and SOC 2 come up in most entry-level GRC interviews
You can learn most of this for free through NIST publications, ISO summaries, and YouTube breakdowns of NIST CSF or ISO 27001. Reading a couple of real regulatory documents end to end will teach you more than a week of general theory. The goal isn’t mastery. It’s being able to hold an intelligent conversation about compliance management in an interview.
Step 2: Pick One GRC Certification for Beginners and Finish It
Certifications are the fastest way to signal credibility when you have no work history to lean on. Don’t try to collect them all at once. Pick the one that matches the door you’re trying to walk through.
Training Camp’s 2026 certification roadmap keeps it simple: lean toward IT audit, go for CISA; focus on risk management, go for CRISC; manage security programs with governance duties, and pursue CISM. Pass one, let the momentum build, then add the next.
For true beginners, CyberArrow’s certification guide notes that ISO 27001 Foundation training and NIST Cybersecurity Framework courses sit at beginner-to-intermediate difficulty and are useful for GRC teams serving U.S. federal or commercial clients.
ISC2’s Certified in Cybersecurity (CC) is another low-cost starting point. It covers security principles, risk and access control basics, and has no experience requirement, which makes it a common first credential for career switchers.
Our guide to entry-level GRC certifications covers CRISC, CISA, ISO 31000, CompTIA Security+, and GRC Professional (GRCP) in more depth, including which ones people from non-IT backgrounds use to break in.
My honest take: if you’re brand new, start with CompTIA Security+, ISC2 CC, or an ISO 27001 Foundation course. They’re cheaper, faster to complete, and still respected. Save CRISC or CISA until you have a job and can meet their experience requirements for full certification.
Step 3: Build a GRC Portfolio That Proves You Can Do the Work
This is the step most beginners skip, and it’s the one that gets interviews. Recruiters scanning resumes for GRC analyst jobs want evidence, not adjectives. Build two or three small projects:
- A mock governance framework for a fictional small business, mapped to ISO 27001 or NIST CSF
- A sample risk register showing how you’d score and prioritize five hypothetical risks
- A one-page compliance audit checklist, such as handling customer data under GDPR
- A SOC 2 readiness gap assessment for a fictional SaaS startup
Put these in a simple portfolio site or a shared PDF. It costs you a weekend and separates you from candidates who only have a certificate and a hope.
Step 4: Write a GRC Analyst Resume Around Transferable Skills
If you’re coming from customer service, you’ve handled documentation and process adherence. From accounting, you already understand controls and audits. From IT support, you’ve dealt with access management and system logs. Reframe these honestly. Don’t invent experience; translate what you did into the language of risk management and compliance.
A few resume tips that work for entry-level GRC roles:
- Put framework names (NIST CSF, ISO 27001, SOC 2) in a skills line so applicant tracking systems catch them
- List portfolio projects under a “GRC Projects” heading, written like job bullets
- Mirror the job title in your summary line, for example, “Aspiring GRC Analyst with ISO 27001 Foundation.”
Step 5: Apply Smart, Not Just Wide
Target smaller companies, MSPs, consulting firms, and GRC platform vendors (such as ServiceNow or Vanta partners) before aiming for Fortune 500 in-house teams. Smaller employers are often more willing to train someone with the right foundation and attitude.
Also look for junior GRC analyst roles under other titles: “Compliance Coordinator,” “Junior Risk Analyst,” “IT Risk Analyst,” or “Security Compliance Associate.” These are often the same job with a different label and a lower experience bar. Many of the best GRC jobs for beginners aren’t labeled “GRC” in the posting at all.
Are There Remote GRC Analyst Jobs for Beginners?
Yes, though fully remote entry-level roles draw more applicants than on-site ones. Remote postings for junior GRC analysts usually ask for 0-2 years of experience and focus on vendor risk questionnaires, evidence collection, and policy upkeep. A hybrid role for your first year is often easier to land and gives you faster mentoring.
What a Typical Week Looks Like Once You’re Hired
A junior analyst’s week usually involves updating a compliance tracker, following up with system owners on overdue evidence requests, and preparing documentation ahead of an upcoming compliance audit. It’s steady, detail-oriented work. The people who thrive in it tend to enjoy checklists and clear processes rather than constant firefighting.
GRC Analyst Career Path: Salary and Requirements by Experience Level
|
Experience Level |
Typical Annual Salary (US) | Common Certifications |
Typical Responsibilities |
|---|---|---|---|
|
Entry-level GRC analyst (0-1 yr) |
$50,800 – $80,350 | Security+, ISC2 CC, ISO 27001 Foundation |
Documentation, evidence collection, basic risk tracking |
|
Early-career (1-3 yrs) |
$63,300 – $88,600 | CRISC or CISA |
Risk assessments, audit support, policy drafting |
|
Mid-level (3-5 yrs) |
$77,400 – $100,500 | CRISC, CISA |
Framework implementation, vendor risk reviews |
|
Senior-level (8+ years) |
$100,600 – $130,000+ | CISM, CGEIT, CISSP |
Program ownership, leadership reporting, strategy |
Common Mistakes Beginners Make
- Chasing every certification at once instead of finishing one and applying.
- Waiting to feel “ready” before applying. Most people who land GRC analyst jobs with no experience apply before they feel fully qualified.
- Ignoring soft skills. This field is full of stakeholder conversations, and communication matters as much as technical knowledge.
- Applying only to titles with “GRC” in them, missing adjacent roles that lead to the same career.
- Not asking about growth paths in interviews. A strong compliance program usually has a clear path from analyst to senior analyst to manager.
A Personal Note
If there’s one thing I wish someone had told me earlier, it’s this: nobody starts a GRC analyst job search feeling fully qualified. Everyone I’ve watched succeed started out feeling slightly like an impostor, filling gaps with one certification, one mock project and one honest conversation at a time.
The field rewards patience and clarity far more than perfection. If you’re a student wondering whether you belong here, you do. Start with one framework, one certification and one small project this month. If you want a structured route, the IT Auditing & GRC Job Seeker’s Package bundles those steps.