Here is a number that might change how you think about your next career move. Nearly 17,000 professionals worldwide have earned the CRMA certification since it launched in 2011, compared to more than 200,000 IIA-certified professionals overall. If you have ever wondered why so few people pursue this credential despite its growing relevance to enterprise risk management, you are about to find out, and the answer might be exactly the opportunity you have been looking for.
The CRMA certification, short for Certification in Risk Management Assurance, is issued by the Institute of Internal Auditors (IIA) and is built specifically for professionals who want to specialize in risk assurance rather than stay generalists. That is the CRMA full form, and it is easy to confuse with other “CRMA” credentials online, so this guide is only about the IIA CRMA. It is a deliberate step for internal auditors and risk professionals who want to go deeper into how organizations identify, assess, and manage risk at a strategic level. This guide covers CRMA eligibility, the CRMA exam pattern and syllabus, CRMA certification cost, and how to prepare in 2027, in plain language and without unnecessary jargon.
What Is the CRMA Certification?
The CRMA (Certification in Risk Management Assurance) is the IIA’s only risk management assurance certification for internal auditors. It validates that you can provide assurance on how an organization governs and manages risk, and advise management and the audit committee on risk management concepts.
Why the CRMA Certification Matters More in 2027
Internal audit has changed. A decade ago, the role was largely about checking whether financial controls were followed correctly. Today, boards and audit committees expect internal auditors to do something much harder: independently evaluate whether an organization’s entire enterprise risk management framework is actually working, not just whether individual controls exist on paper.
This shift is exactly what the CRMA certification was designed to address. It signals to employers that an internal auditor can step beyond routine compliance checks and provide genuine assurance on how risk is governed, assessed, and managed across an organization. CRMA holders are increasingly well positioned for Chief Audit Executive, Internal Audit Director, and risk assurance leadership roles at mid-to-large organizations.
What makes this particularly relevant right now is the regulatory environment. Organizations across financial services, healthcare, insurance, and manufacturing are under more pressure than ever to demonstrate that their risk oversight is not just a checkbox exercise. The CRMA certification positions the holder as someone who can credibly assess that oversight and advise leadership on where the gaps actually are.
CRMA Eligibility and Requirements in 2027
The biggest change many older guides miss: the IIA no longer requires the CIA as a prerequisite for the CRMA. Eligibility now depends on your education and internal audit experience.
|
Education level |
Experience required |
|---|---|
|
Master’s degree (or higher) |
1 year of internal audit experience |
|
Bachelor’s degree |
2 years of internal audit experience |
|
Active Internal Audit Practitioner (IAP) |
5 years (or 1–2 years with a degree) |
|
No degree |
5 years, with 2 of them in the last 3 years |
Qualifying experience can come from internal audit, risk management, compliance, quality assurance, external audit, or internal control. You can sit for the CRMA exam before you complete the experience requirement, but you must pass the exam within two years of being accepted into the program.
Who the CRMA Certification Is Really For
Removing the CIA prerequisite made the CRMA more accessible, but it is still not an entry-level qualification. It is a specialization for people who already work in audit or risk.
In practical terms, this credential tends to attract a specific group of professionals. Senior internal auditors who are ready to move into risk-focused leadership roles make up a large portion of candidates. Audit managers and directors overseeing risk-based audit plans pursue it to formalize expertise they are already applying daily. Enterprise risk management professionals with an internal audit background use it to bridge the gap between the two functions, which are increasingly expected to work closely together. Risk consultants serving regulated industries such as banking, insurance, and healthcare also pursue the CRMA because clients in those sectors value the credential as a differentiator.
If you are just starting out as an internal auditor, the realistic path is to build experience in risk-related audit work first, and consider the CIA or IAP for broader internal audit foundations before specializing with the CRMA.
CRMA vs CIA: Which Should You Choose?
|
Factor |
CRMA |
CIA |
|---|---|---|
|
Focus |
Risk management assurance and governance |
Full scope of internal auditing |
|
Exams |
1 exam, 120 questions, 150 minutes |
3 exam parts |
|
CIA required first? |
No |
— |
|
Best for |
Auditors and risk professionals specializing in ERM assurance |
Building a broad internal audit career |
Many professionals hold both. The CIA proves broad internal audit competence; the CRMA proves you can assure an organization’s risk management specifically.
CRMA Exam Pattern: What You’re Actually Being Tested On
CRMA syllabus: three domains, and the weighting matters
The CRMA exam is built around three core domains, and knowing how much each one counts can completely change how you plan your study time.
Domain 1: Internal audit roles and responsibilities (20%) This portion covers the foundational duties and positioning of internal audit in risk management, including coordinating assurance and building a risk assurance map. It makes up the smallest slice of the exam.
Domain 2: Risk management governance (25%) This domain looks at how risk management is governed at an organizational level, including governance and control frameworks, risk culture, and how risk is integrated into strategy.
Domain 3: Risk management assurance (55%) This is by far the largest domain, and for good reason. It covers risk assessment approaches, data analytics, risk-based internal audit planning, IT and cybersecurity risk, and reporting to the board. The heavy weighting reflects exactly what the credential is meant to prove: that you can genuinely assess whether an organization’s risk management processes work in practice, not just on paper.
CRMA exam format and passing score
The CRMA exam has 120 questions and a 150-minute time limit, taken in a single sitting at a Pearson VUE test center. Questions include multiple choice and other formats such as multiple response and scenario-based items. You need a scaled score of 600 out of 750 to pass. Since April 1, 2027, the IIA issues a single official result within three weeks of your exam date.
CRMA pass rate
The CRMA pass rate is commonly reported at around 45 percent, roughly on par with the first part of the CIA exam. This is a real shift from earlier years when the CRMA had a reputation for being easier, mainly because the exam was revised to test deeper application rather than recall.
The COSO Framework is non-negotiable.
Throughout the exam, you’re expected to apply frameworks central to the profession, especially the COSO Framework for internal control and enterprise risk management, alongside ISO 31000. Understanding how they structure risk assessment, control environments, and governance isn’t optional. It’s a core part of being genuinely exam-ready. Note that the CRMA syllabus is currently supported by the IIA’s 2017 Standards.
CRMA Certification Cost in 2027
Cost is one of the most practical considerations, and it depends on your IIA membership status and location.
|
Fee |
IIA member |
Non-member |
|---|---|---|
|
CRMA application fee |
$100 |
$220 |
|
CRMA exam registration fee |
$465 |
$610 |
|
Total official fees |
$565 |
$830 |
|
Exam reschedule/cancellation |
$75 |
$75 |
|
Exam registration extension |
$100 |
$100 |
|
Program eligibility extension |
$275 | $275 |
On top of official fees, budget for IIA membership dues (which vary by country), study materials such as the IIA’s CRMA Study Guide and Practice Questions, and a possible retake. Pricing outside North America may differ, so check with your local IIA institute.
CRMA Certification at a Glance
|
Factor |
Details |
|---|---|
|
Full form |
Certification in Risk Management Assurance |
|
Issuing body |
Institute of Internal Auditors (IIA) |
|
CIA required? |
No |
|
Experience |
1–5 years, depending on education |
|
Exam |
120 questions, 150 minutes |
|
Syllabus domains |
Internal audit roles (20%), risk management governance (25%), risk management assurance (55%) |
|
Passing score |
600 out of 750 |
|
Pass rate |
Around 45% (commonly reported) |
|
Official fees |
$565 member / $830 non-member |
|
Program window |
2 years from acceptance |
|
Result turnaround |
Within 3 weeks of the exam date |
|
CPE requirement |
20 hours annually, including 2 hours of ethics |
|
Holders |
Nearly 17,000 worldwide |
How to Prepare for the CRMA Exam
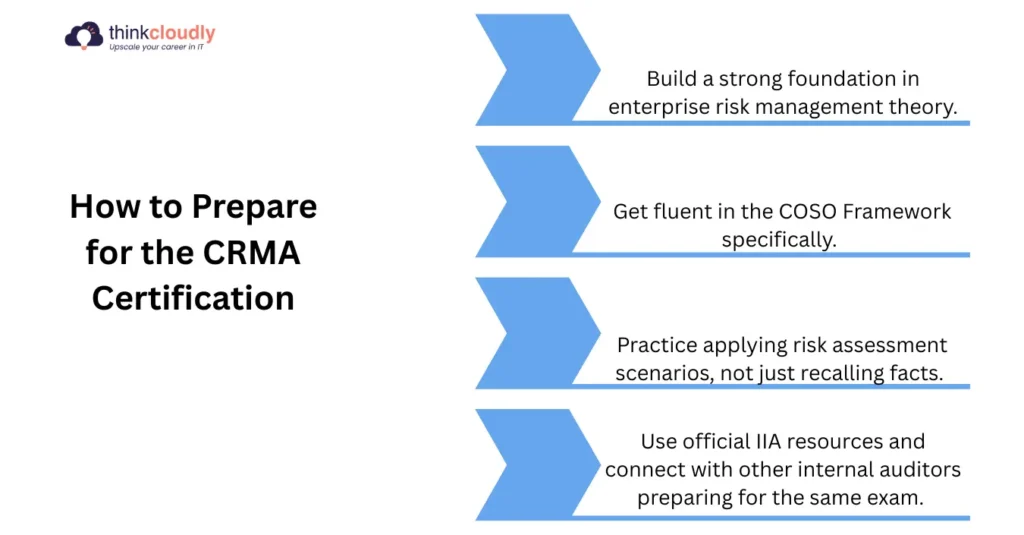
Build a strong foundation in enterprise risk management theory
Before diving into CRMA practice questions, spend time genuinely understanding how an enterprise risk management framework operates end to end, from risk identification through to monitoring and reporting. The exam tests application, not memorization, so understanding why frameworks are structured the way they are matters more than knowing definitions.
Get fluent in the COSO Framework specifically
Because the COSO Framework underpins so much of how risk management assurance is assessed globally, candidates who treat it as a core study area rather than a side topic consistently report feeling more prepared for the assurance-focused questions that dominate the exam.
Practice risk assessment scenarios, not just recall
Given that risk assessment is central to the largest exam domain, work through realistic scenarios where you have to judge whether a risk response is adequate, identify gaps in a control environment, or evaluate the quality of an organization’s risk reporting. This scenario-based thinking is exactly what the exam rewards.
Use the official CRMA study guide and practice questions
The IIA publishes the CRMA Study Guide and Practice Questions (3rd Edition) and an aligned review course, plus a demo of the exam’s question types. With 120 questions in 150 minutes, you have about 75 seconds per question, so timed practice matters. Candidates who supplement official materials with peer study groups or structured review courses tend to perform more consistently than those relying on a single resource.
Maintaining the CRMA Certification
Once earned, the CRMA certification requires ongoing maintenance to stay active. Holders must report 20 hours of continuing professional education annually, with at least two hours focused on ethics. If you also hold the CIA, plan your CPE so that qualifying hours count toward both credentials.
Is the CRMA Certification Worth It?
For internal auditors and risk professionals who want to move into senior risk assurance roles, yes. With the CIA prerequisite removed, the CRMA is now faster and cheaper to reach than before, yet still held by a small group worldwide. That scarcity is the value. If your career is focused on general audit rather than risk, the CIA may give a broader return first.
Conclusion
The CRMA certification occupies a specific and increasingly valuable space in the internal audit world. It is not meant to be a first step. But for internal auditors and risk professionals who want formal recognition of their ability to provide genuine assurance on how an organization manages risk, it is one of the clearest signals available in 2027.
With eligibility now open to candidates without the CIA, a demanding exam pass rate, and content that requires deeper application of frameworks like COSO, the CRMA certification is becoming a more meaningful differentiator, not a less relevant one. For internal auditors looking to move into senior risk-focused roles, advise audit committees, or position themselves as trusted voices on enterprise risk management, the CRMA remains one of the most direct paths to get there.