A cyberattack now takes attackers roughly zero days to exploit a freshly published vulnerability, yet it still takes most companies well over two hundred days to even notice they have been breached. Sit with that gap for a second. If a criminal can walk through an open door in hours, and the people guarding the building only realize the door is open months later, what does that tell you about who is actually winning right now?
This is exactly the question that pushed me toward writing about incident response training for beginners, and it is the question every aspiring incident response analyst eventually has to answer for themselves. I still remember my first real incident. I was a junior analyst, two weeks into a new job, staring at a screen full of alerts that all looked urgent and none of which I understood.
My senior teammate calmly walked me through triage, and by the end of that night I realized something simple: knowledge alone does not make you useful during a breach. Practiced, structured training does. That night shaped how I think about this career path, and it is the lens I am using to write this guide. If you are new to the field, start with our explainer on what incident response is, then come back here for the training path.
Near-instant exploitation on one side and 241 days to identify and contain a breach on the other are not abstract statistics for future readers to shrug at. They describe a labor market that is actively short on trained people who can walk into chaos and bring order to it. That is exactly what structured, hands-on incident response training is designed to produce.
Why Incident Response Training Matters More in 2027 Than Ever Before
Ransomware has not slowed down; it has industrialized. Recent 2027 data shows global ransomware damages sitting near $57 billion a year, with attack volume climbing even as fewer victims actually pay, according to figures compiled by StationX from sources including the FBI’s Internet Crime Complaint Center and the Sophos State of Ransomware survey.
CrowdStrike’s Global Threat Report also shows that 79% of initial access attacks are now malware-free, relying on stolen credentials and legitimate tools instead of obvious malicious code. That shift matters for anyone starting out: today’s analysts need more than antivirus knowledge. They need genuine cyber incident response training covering behavioral detection, log analysis, and calm decision-making under pressure.
The workforce numbers reinforce the urgency. ISC2’s Cybersecurity Workforce Study found that organizations with critical or significant skills gaps are nearly twice as likely to suffer a material breach, and that lack of budget has now overtaken lack of talent as the top staffing barrier.
Companies increasingly cannot hire their way out of the problem; they need to train the people they already have, and newcomers need a real, credible on-ramp into the profession. This is where a structured training pathway, built progressively from fundamentals to advanced analyst skills, becomes the practical answer rather than a nice-to-have.
Trained analysts are also the people who translate a single bad incident into long-term risk mitigation, rather than letting the same weakness get exploited twice.
The Incident Response Lifecycle Every Analyst Must Know
Every serious incident response training program is built around the lifecycle defined by NIST in SP 800-61. The classic version has four phases:
-
Preparation: building the incident response plan, playbooks, tooling and trained team before anything goes wrong.
-
Detection and analysis: spotting suspicious activity in SIEM, EDR and log data, then confirming whether it is a real incident and how severe it is.
-
Containment, eradication and recovery: isolating affected systems, removing the attacker’s foothold and restoring operations safely.
-
Post-incident activity: the lessons-learned review that turns one incident into stronger defenses.
NIST’s 2025 revision, SP 800-61 Rev. 3, maps incident response onto the six functions of the Cybersecurity Framework 2.0, but the four phases above remain the way most SOC teams and interviewers talk about the incident response process. If you can explain each phase with a real example, you are already ahead of most beginners.
The Skills Gap Nobody Is Talking About Enough
ISC2 puts the global cybersecurity workforce shortfall at 4.8 million roles, and digital forensics and incident response (DFIR) is named specifically among the areas where 90% of security teams report gaps. What strikes me most is not the size of that number but where the gap sits.
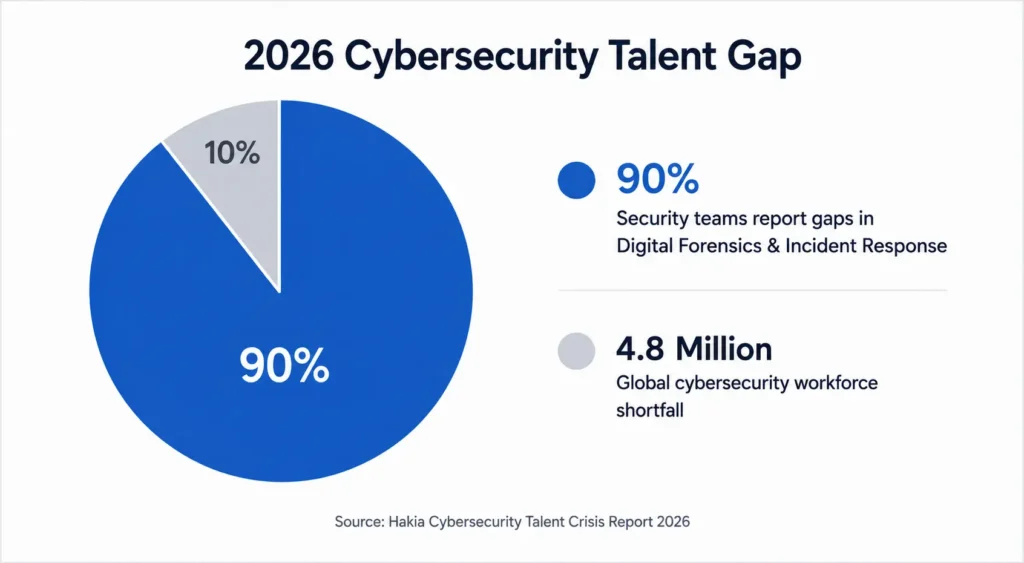
It is not entry-level headcount that is missing; it is people who can perform disciplined forensic investigations, apply cyber forensics methods under pressure, and make a defensible containment decision at 2 a.m. without panicking. That is a specific, learnable set of incident response skills, and one that generic IT courses simply do not build.
This is also why career changers are becoming such a large part of the field. Recent ISACA data shows that 46% of current cybersecurity professionals moved in from non-security roles entirely.
You do not need a computer science degree to start. What you need is a training path that respects where you are starting from, teaches vulnerability assessment alongside cyber forensics, and builds you up methodically, module by module, toward real analyst competence.
What a Beginner-to-Analyst Incident Response Training Path Looks Like
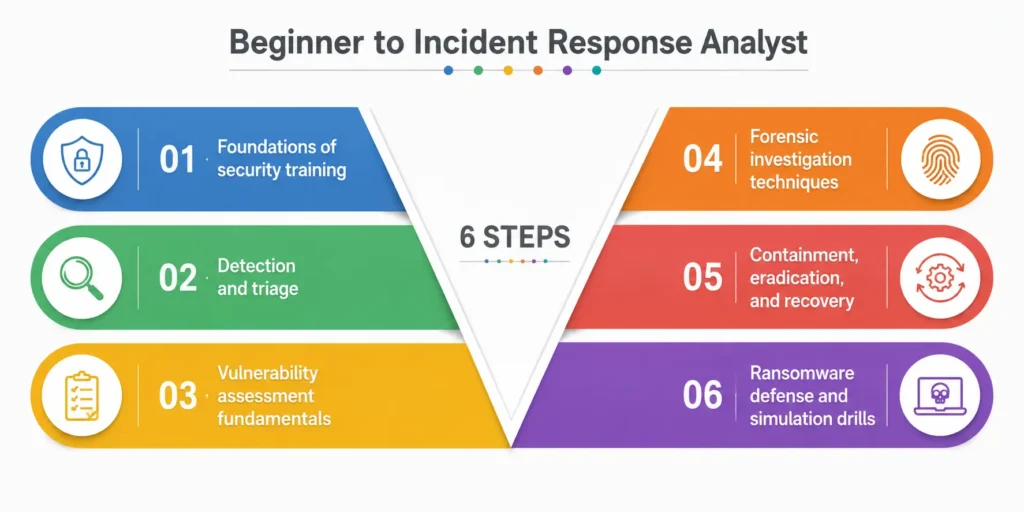
Most people picture incident response as dramatic movie-style hacking battles. In reality, it is closer to disciplined detective work layered with technical precision, drawing heavily on cyber forensics rather than guesswork. A sound analyst training program, much like good SOC analyst training, usually moves through these stages:
-
Foundations of security training: understanding networks, operating systems, common attack vectors, and how to read logs before anything else. This is the bedrock; skipping it creates analysts who can follow a checklist but cannot reason about an unfamiliar attack.
-
Detection and triage: learning to separate genuine threats from noise, using SIEM tools such as Splunk, EDR alerts and log data to prioritize what actually needs attention first.
-
Vulnerability assessment fundamentals: learning how to scan systems, interpret findings, and understand which weaknesses attackers are most likely to exploit, since a thorough vulnerability assessment and a fast response are two sides of the same coin.
-
Forensic investigation techniques: preserving evidence correctly, building attack timelines, and understanding how a forensic investigation must hold up if it is ever needed for legal or regulatory review.
-
Containment, eradication, and recovery: the applied stage where trainees follow an incident response playbook to isolate systems, remove threats, and restore operations without destroying evidence in the process.
-
Ransomware defense and tabletop exercises: realistic incident response tabletop exercises and live-fire drills where trainees handle a ransomware incident response scenario, because reading about ransomware defense and actually managing one under time pressure are very different experiences.
Notice that this pathway blends cyber forensics with hands-on decision-making rather than treating them as separate subjects. That blend is precisely what separates a credential on paper from someone who can be trusted during a live incident.
Building Real Competence: Risk Mitigation and Beyond
Good incident response training does not stop once an incident is resolved. Analysts also need to think about risk mitigation as an ongoing discipline, translating what was learned from an attack into stronger defenses for next time.
Risk mitigation built from real incident lessons is not just a compliance exercise; it has a measurable financial return. Regular security training refreshers keep that risk mitigation habit alive instead of letting lessons fade after a few quiet months.
This is also where good security training culture matters. IBM’s data shows that breaches identified and contained within 200 days cost organizations significantly less than those that drag on longer, and the difference often comes down to whether staff were trained to recognize early warning signs.
A well-trained junior analyst who notices something odd in week one can save an organization more money than an expensive tool nobody knows how to interpret. That, in my experience, is the strongest argument for structured training over relying on tools alone.
2027 Incident Response Snapshot: Key Data at a Glance
|
Metric |
2026-2027 Figure |
Source |
|---|---|---|
|
Global average data breach cost |
$4.44 million | |
|
Mean time to identify and contain a breach |
241 days |
IBM Cost of a Data Breach Report 2025 |
|
Breaches involving ransomware |
44% of all breaches |
Verizon DBIR |
|
Global cybersecurity workforce gap |
4.8 million roles |
ISC2 Cybersecurity Workforce Study |
|
Organizations hit by a security event tied to skills gaps |
88% |
ISC2 2025 Workforce Study |
|
Initial access attacks that are malware-free |
79% |
CrowdStrike Global Threat Report |
|
Cost savings from extensive AI/automation use in response |
~$1.9 million per breach |
IBM Cost of a Data Breach Report 2025 |
These figures make one thing obvious: incident response training is not a soft skill add-on anymore. It sits directly on the line between a contained, low-cost incident and a nine-figure organizational crisis.
Incident Response Certifications Worth Considering
Training builds the skill; a certification proves it to an employer who has never seen you work an incident. The most recognized options, roughly from entry level to advanced:
-
CompTIA Security+: the common foundation most hiring managers expect before IR-specific credentials.
-
CompTIA CySA+: focused on detection, analysis, and response; a natural fit for SOC and junior IR roles.
-
EC-Council ECIH (Certified Incident Handler): built around the incident handling process end to end.
-
GIAC GCIH (Certified Incident Handler): widely respected for hands-on incident handling and attacker techniques.
-
GIAC GCFA (Certified Forensic Analyst): for analysts moving deeper into DFIR and enterprise forensics.
A certification without practice rarely survives a technical interview. Pair any incident response certification with lab work, and review common incident response interview questions before you apply.
How to Choose the Right Incident Response Course
When evaluating any incident response course or training program, look for a few non-negotiables. It should combine theory with live-fire simulation, not just slides. It should cover vulnerability assessment and forensic investigation as connected disciplines rather than isolated topics and treat cyber forensics as a practiced skill rather than a single lecture slide.
It should include realistic ransomware defense scenarios and tabletop exercises, since ransomware remains the dominant threat organizations face in 2027. And it should be taught by people who have actually worked incidents. Analysts who train under realistic pressure perform far better when a real breach happens, because the panic of “this is not a drill” has already been rehearsed once.
It is also worth remembering that cyber forensics and incident handling are not purely technical disciplines. Good analysts learn to communicate clearly under pressure, document decisions defensibly, and coordinate with legal, communications, and leadership teams during a crisis. No amount of tool knowledge substitutes for that composure, and it is usually the hardest thing for a beginner to build without structured, repeated practice.
Conclusion
Going back to that opening question: if attackers can exploit a new weakness in essentially zero days while most organizations take 241 days on average to identify and contain a breach, the honest answer is that skilled people, not just software, are what closes that gap.
Solid incident response training turns a nervous beginner into a calm, capable incident response analyst who can read the signals, contain the damage, and help an organization recover faster and cheaper.
The 2027 data is consistent across every major report: breaches are getting harder to prevent entirely, but organizations with well-trained teams detect them faster, spend less recovering from them, and suffer less repeat damage.
Whether you are just starting out or trying to sharpen an existing skill set, investing in real, structured professional preparation remains one of the most practical decisions you can make for your career and for the organizations that will eventually depend on you during their worst day.
Solid security training and rehearsed ransomware defense do not just protect a business; they protect the people whose job it is to answer the phone at 2 a.m.
If you are looking for a place to start, Thinkcloudly’s SOC Analyst program runs a hands-on training track that walks learners from the fundamentals all the way through live incident simulations, forensic exercises, and mentor-led review sessions. Alongside the core coursework, the program includes practice labs, career guidance calls, and access to instructors who have actually worked live incidents, which tends to make the jump from the classroom to a real analyst desk a lot less intimidating.